Twenty two years designing, securing, and modernizing the networks that run railways, utilities, and financial platforms across North America.
Introduction
Architecture, not just configuration
Most network problems are not really network problems. They are the accumulated cost of decisions made without a clear design, documented under time pressure, and inherited by whoever came next.
ABC Network Consultants works at the layer above the command line. We produce the architecture packages, migration plans, and security designs that let large organizations change complex infrastructure without breaking it — and prove to auditors and governance boards that the change was sound.
The work is led by a CCIE#21944 (Security), CISSP-certified security architect with two decades of hands-on enterprise experience, from campus switching to multi-cloud zero trust.
Services
Network architecture and design
Campus, data centre, and hybrid cloud design built on validated reference architectures. Wireless modernization, large-scale switching refresh, routing design across BGP, OSPF, and EVPN fabrics, and network management platform deployment.
Security architecture and governance
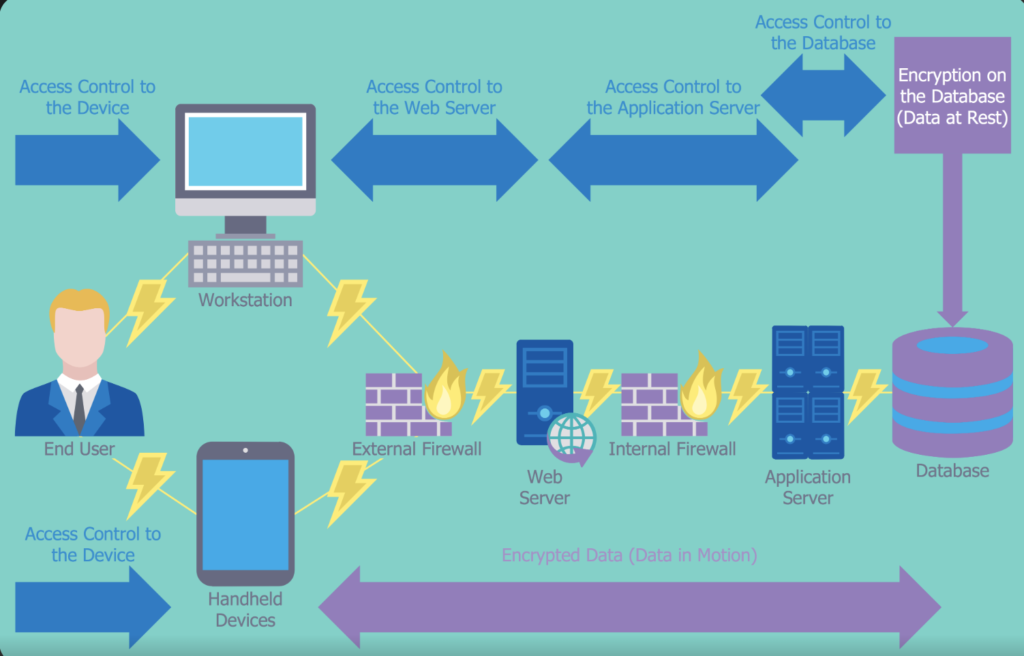
Formal security architecture packages built for architecture review boards and third-party risk assessments. Firewall and segmentation design, zero trust and SASE strategy, identity federation, and requirements documentation written to withstand scrutiny.
Cloud and hybrid connectivity
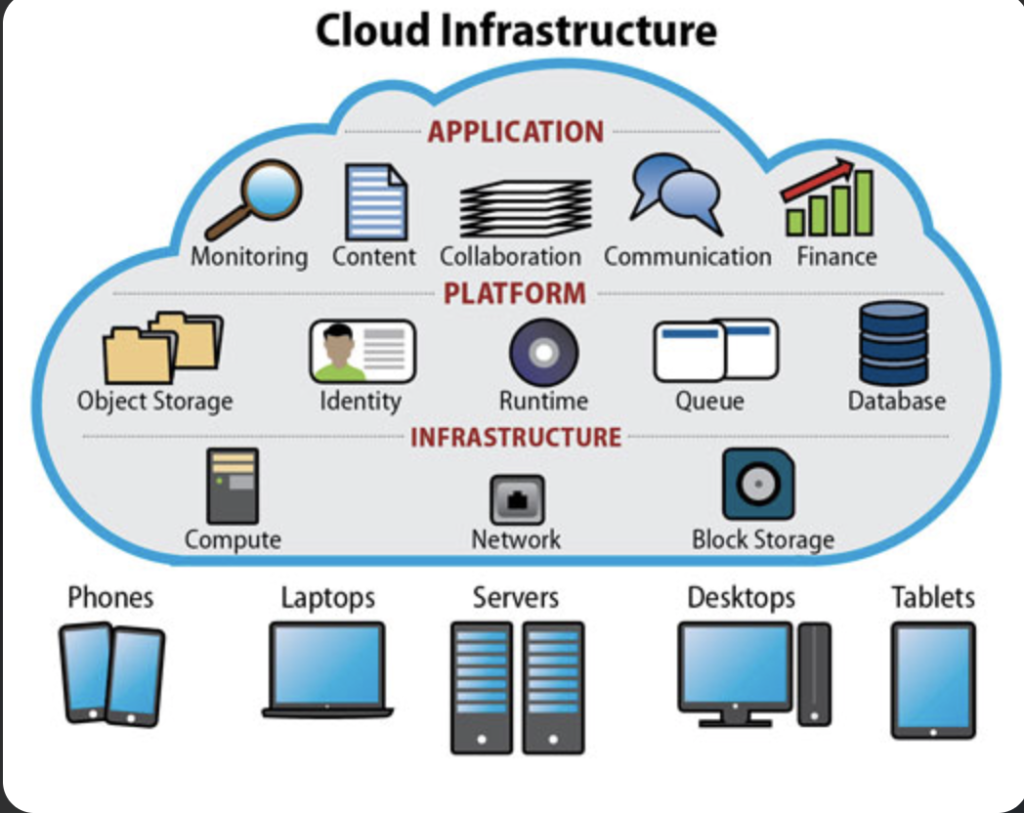
Azure Virtual WAN and hybrid routing design, GCP and AWS network security, secure interconnect between on-premises estates and cloud workloads, and cloud-native firewall placement that reflects real traffic paths.
Migration and operational delivery
Method of procedure documents detailed enough for a junior engineer to execute unaided. Firewall platform migrations, remote access VPN modernization, certificate lifecycle programs, and phased upgrade rollouts with tested rollback.
Platform expertise
Deep bench across the platforms you already run
We do not arrive with a single vendor’s answer. The work spans the platforms that actually make up enterprise networks:
- Firewalls and NGFW
- Cisco ASA, Cisco Firepower (FTD/FMC), Palo Alto/Panorama, Check Point, Juniper SRX
- VPN Technologies: IPSec, SSL, AnyConnect
- AAA, RADIUS, TACACS+, Cisco ISE
- Application delivery and WAF — F5 BIG-IP across LTM, APM, ASM, AFM, and BIG-IQ
- Identity and access — Cisco ISE, 802.1X, Microsoft Entra ID and SAML federation, RADIUS and TACACS+
- Secure access and SASE — Zscaler Internet Access and Private Access, Cisco Umbrella, remote access VPN
- Cloud and Tools
- AWS (network and security components), GCP
- SolarWinds, Splunk, Cisco DNAC, Tufin, BlueCat DNS
- Routing, switching, and services — Cisco Catalyst Center, BGP, OSPF, MPLS, VXLAN and EVPN, BlueCat and Infoblox DNS and IPAM
- Documentation & Operations
- HLD/LLD, MOPs, Visio diagrams
- Tier-3 support, change & incident management, on-call support
- Wireless – Cisco WLC, LWAP, Aruba Wireless Controllers and Access Points
- SD-WAN – Aruba Silver Peak SD-WAN (enterprise deployments and migrations), Cisco Viptela
- Data Center
- Cisco Nexus (9K / 7K / 5K / 3K), Catalyst Switches
- Data Center network design, migrations, and operations
Sector experience
Our principal’s engagements span:
- Banking and financial services — Network and security engineering for major Canadian banks and insurers, including branch-scale LAN/WAN design across 1,500+ locations, SD-WAN modernization, and firewall and load balancer estates in regulated environments.
- Loyalty and consumer platforms — Remote access modernization, application delivery, and certificate lifecycle management for high-transaction consumer platforms.
- Telecommunications — Greenfield headquarters network design, wireless architecture, zero-trust secure web gateway rollout, and firewall policy consolidation for a national carrier.
- Retail, grocery and pharmacy — Security and network operations across store estates, distribution centres, and data centres, including managed-service transitions and proxy and firewall policy cleanup.
- Technology and cloud providers — Cloud-to-cloud firewall migration, infrastructure consolidation following corporate acquisition, and Tier-3 escalation support for enterprise security platforms.
- Rail and transportation — Security architecture for freight rail and regional transit, delivered through formal architecture governance gates.
- Energy and utilities — Cloud networking and segmentation design for electric utility environments, with attention to OT boundaries and regulatory expectations.
- Manufacturing and food production — Full network refresh programs covering Layer 2/3 redesign, next-generation firewall deployment, wireless site surveys, and structured cabling.
- Healthcare — HIPAA-aligned system design for handling protected health information, from mobile capture through secure delivery.
What you actually receive
Documentation that survives handover.
Every engagement produces artifacts your team can use after we leave — design documents, method of procedure runbooks, requirements workbooks, and diagrams that match what is really deployed.
Designs that pass governance.
Architecture packages structured for review boards, third-party risk assessment, and vendor evaluation, using the conventions your process already expects.
Honest scoping.
Effort estimates broken down by workstream and activity, with assumptions stated plainly and open questions listed rather than buried.
Change you can roll back.
Phased cutover plans with validation checkpoints, tested rollback paths, and pre-change checks that catch the routing asymmetries and stale configuration that derail migrations.
Let’s talk about what you are trying to change
Whether you are planning a platform migration, preparing an architecture submission, or trying to get a stalled project moving again, a short conversation is usually enough to tell whether we can help.
Working with clients across North America.